
What Is Identity and Access Management in Security?
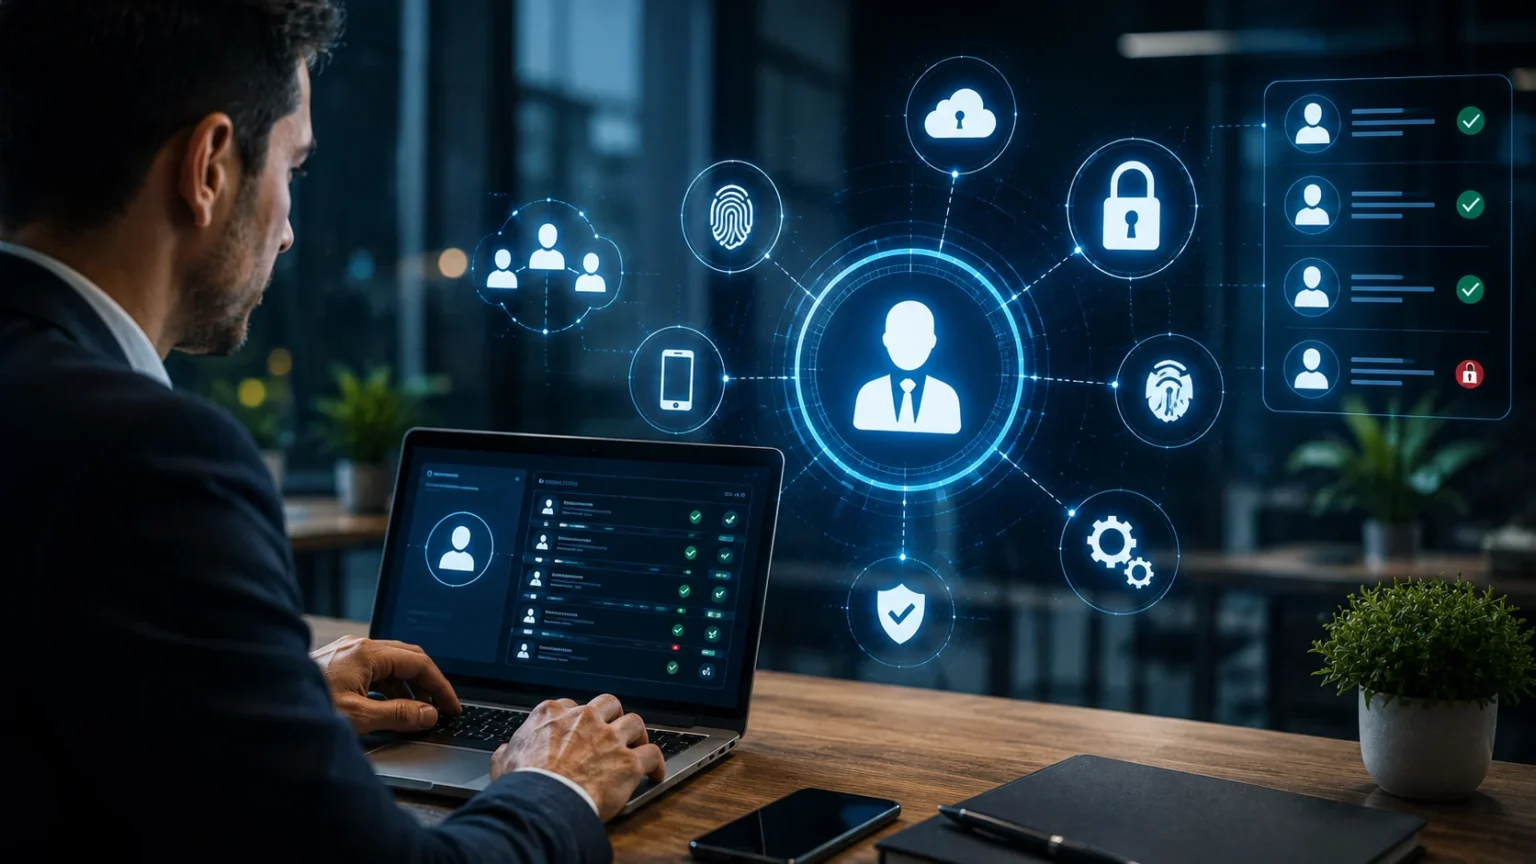
Identity and Access Management, commonly called IAM, has become a core part of modern cybersecurity because organizations can no longer protect information simply by placing systems behind a network perimeter. Employees, contractors, customers, applications, cloud services, devices, and automated workloads may all need access to digital resources. IAM helps businesses determine who or what is requesting access and whether that identity should be allowed to perform a particular action.
The concept sounds simple, but access management has become increasingly important as organizations adopt cloud computing, remote work, software-as-a-service platforms, mobile applications, and distributed IT environments. A single employee may interact with dozens of business systems every week, while administrators and automated services may hold highly sensitive permissions. Without effective identity security, compromised credentials or excessive access rights can quickly expose valuable systems and data.
A strong IAM strategy combines technologies, policies, and processes to manage digital identities throughout their lifecycle. It includes activities such as creating user accounts, authenticating users, assigning permissions, enforcing multifactor authentication, reviewing access, managing privileged accounts, and removing permissions when they are no longer required. These controls help organizations reduce unauthorized access while allowing legitimate users to perform their work efficiently.
Understanding identity and access management is useful for businesses of every size because cyberattacks frequently target user accounts and credentials. IAM does not eliminate every security risk, but it creates a structured approach to controlling access to applications, networks, cloud resources, and sensitive information. This guide explains how IAM works, its major components, its role in Zero Trust security, and the practices organizations can use to strengthen identity protection.
What Is Identity and Access Management?
Identity and Access Management is a cybersecurity framework used to manage digital identities and control their access to organizational resources. In practical terms, IAM helps answer two essential questions: who is requesting access, and what is that person or system allowed to do? Organizations use IAM technologies to manage access to applications, databases, files, networks, cloud platforms, and other digital services.
An identity within an IAM system does not always represent a human employee. Digital identities may belong to customers, contractors, administrators, devices, applications, service accounts, automated systems, or increasingly intelligent software agents. Each identity can be assigned attributes and permissions that determine which resources it can access and which actions it can perform within those resources.
Access management focuses on enforcing those permissions after an identity has been recognized. For example, two employees might successfully sign in to the same company system, but one may only be allowed to view records while another is authorized to modify them. IAM makes this distinction possible by connecting verified identities with defined access policies and authorization rules.
Modern IAM systems usually combine identity directories, authentication mechanisms, authorization policies, access governance, monitoring, and lifecycle management. Together, these capabilities help businesses provide legitimate users with appropriate access while limiting exposure to sensitive information. The ultimate goal is not simply to block access but to provide the right access to the right identity at the right time.
Why Identity and Access Management Is Important
One of the biggest reasons IAM is important is that user credentials can become an attractive path into organizational systems. Attackers may attempt phishing, credential theft, password guessing, session hijacking, or other techniques to impersonate legitimate users. Strong identity security makes it more difficult for a stolen password alone to provide unrestricted access to valuable resources.
IAM also helps control excessive permissions. Employees sometimes accumulate access as they move between departments, take on temporary projects, or receive additional responsibilities. If old permissions are never removed, users may eventually have access to systems they no longer need. This unnecessary access increases the potential impact of compromised accounts, mistakes, and insider threats.
Modern organizations also need IAM because their technology environments are increasingly distributed. Employees may access cloud applications from home, customer data may exist across several platforms, and businesses may rely on external contractors or partners. Traditional network-based security controls alone cannot reliably determine whether every access request is legitimate, making identity an important security control point.
Effective identity and access management can also improve operational efficiency. Centralized authentication, automated account provisioning, single sign-on, and role-based access controls can make it easier for employees to access approved resources without repeatedly requesting manual assistance. Well-designed IAM therefore supports both stronger cybersecurity and a smoother user experience.
How Identity and Access Management Works
IAM usually begins by creating or recognizing a digital identity. When a new employee joins a company, for example, an identity may be created within the organization’s directory or identity provider. Information such as department, job role, location, manager, and employment status can be associated with the account and later used to determine appropriate access.
The next stage is authentication, which verifies that someone attempting to use an identity is genuinely authorized to do so. Authentication may involve a password, security key, biometric verification, authenticator application, passkey, or multiple factors. Strong authentication reduces the likelihood that possession of a single compromised credential will be enough to access protected systems.
After authentication comes authorization. Authorization determines which applications, files, systems, or actions the authenticated identity is permitted to access. IAM platforms can evaluate roles, policies, group membership, device information, risk signals, location, and other conditions before granting access. This allows organizations to apply more granular access controls instead of treating every authenticated user the same way.
IAM systems also continue managing identities after access has been granted. Permissions may change when employees move roles, administrators can review access, and accounts should be disabled when users leave the organization. Logs can record important access activity for monitoring and investigation. This identity lifecycle approach helps prevent outdated accounts and permissions from remaining active indefinitely.
Authentication vs Authorization in IAM
Authentication and authorization are closely connected concepts, but they perform different security functions. Authentication verifies identity, while authorization determines permissions. A simple example is entering a secure building: presenting a valid employee credential proves who you are, but different access rules may determine which rooms you are allowed to enter.
In digital environments, authentication normally takes place during sign-in. A user may provide a password and approve a second authentication factor before an identity provider confirms the account. Once authentication is successful, the application receives enough information to recognize the user and continue evaluating whether access should be granted.
Authorization happens after identity verification. The system checks what the authenticated user is allowed to do. A marketing employee may have permission to view analytics reports but not change payroll information, while a finance manager may receive different privileges. These restrictions are commonly enforced through roles, policies, groups, or resource-level permissions.
Understanding this distinction is important because successful authentication should never automatically mean unlimited access. If every authenticated user receives broad privileges, one compromised account can create significant damage. Strong IAM combines reliable identity verification with carefully controlled authorization so that authenticated users receive only the access necessary for their responsibilities.
What Are the Main Components of IAM?
Identity management is one of the foundational components of IAM. Organizations need a reliable method for creating, storing, updating, and removing digital identities. Identity directories and identity providers can maintain information about users, groups, roles, and account attributes while helping other systems determine who is attempting to access them.
Authentication is another essential component. IAM environments may support passwords, multifactor authentication, passkeys, hardware security keys, biometrics, and other methods for verifying identities. Organizations often strengthen authentication for sensitive applications or high-risk situations instead of relying entirely on traditional usernames and passwords.
Authorization and access control determine what an authenticated identity can do. Organizations may use role-based access control, attribute-based policies, conditional access, or resource-specific permissions to limit access. These controls help enforce the principle of least privilege by granting only the permissions genuinely required for a task.
Identity governance completes the broader IAM picture by helping businesses review and manage access over time. Governance capabilities may include access certifications, approval workflows, account provisioning, permission reviews, separation-of-duties controls, and audit reporting. These features help prevent access rights from becoming outdated or unnecessarily broad as employees and business requirements change.
What Is Identity Lifecycle Management?
Identity lifecycle management refers to managing digital identities from the moment they are created until they are eventually removed. For employees, this process often begins during onboarding when accounts are created and appropriate applications are assigned. The objective is to provide necessary access quickly without granting permissions that the employee does not need.
Identity management continues throughout the person’s relationship with the organization. When an employee changes department, receives a promotion, joins a temporary project, or assumes different responsibilities, access should be reviewed. Permissions that are no longer needed should be removed instead of simply adding new access on top of existing privileges.
Offboarding is particularly important because former employees should not retain access to company systems. Organizations can reduce this risk by connecting IAM processes with human resources systems and automatically disabling accounts when employment ends. Access tokens, active sessions, application permissions, and privileged credentials may also need to be revoked.
Lifecycle management applies to non-human identities as well. Service accounts, applications, machines, and automation tools can accumulate permissions that eventually become unnecessary. Organizations should track ownership, purpose, usage, and expiration for these identities so abandoned accounts do not quietly remain active and create long-term security exposure.
What Is Role-Based Access Control?
Role-Based Access Control, commonly known as RBAC, assigns permissions according to job functions rather than configuring every user’s permissions individually. Instead of manually granting dozens of permissions to every employee, administrators can define roles such as customer support representative, finance analyst, developer, or system administrator and assign appropriate permissions to each role.
RBAC can simplify access management significantly as organizations grow. When a new employee joins the finance department, for example, administrators may assign an approved finance role rather than building permissions from the beginning. This approach can improve consistency and reduce the chance that individual accounts receive unusual or unnecessary access.
Roles should still be designed carefully. If a role contains more permissions than most users actually require, assigning that role broadly can weaken the principle of least privilege. Organizations may therefore create different roles according to responsibilities, seniority, geographic requirements, or specific operational tasks rather than relying on a small number of overly powerful roles.
Regular role reviews are also necessary because businesses change over time. Applications are introduced, responsibilities evolve, and departments may reorganize. Access that made sense when a role was originally created may no longer be appropriate several years later. Reviewing role definitions and actual usage helps organizations maintain cleaner and more secure authorization models.
The Principle of Least Privilege in IAM
Least privilege is one of the most important principles in identity and access management. It means that users, applications, and systems should receive only the minimum permissions required to complete legitimate responsibilities. A person who only needs to read information, for example, should not automatically receive permission to delete or modify that information.
Applying least privilege helps reduce the potential impact of compromised accounts. If an attacker gains control of an account with limited permissions, the attacker may have fewer opportunities to access sensitive systems or move throughout the environment. Broad administrative permissions, by contrast, can turn a single compromised account into a much more serious security incident.
Least privilege should apply to temporary access as well as permanent permissions. Administrators or developers may occasionally require elevated privileges to perform specific tasks, but they do not necessarily need those privileges continuously. Just-in-time access can provide elevated permissions for a limited period and automatically remove them when the approved task is complete.
Maintaining least privilege requires continuous attention because permissions tend to expand as users change responsibilities. Access reviews, automated recommendations, privilege monitoring, and identity governance can help identify unused permissions. Organizations should treat access rights as something that must be regularly justified rather than permanently retained once they have been granted.
What Is Privileged Access Management?
Privileged Access Management, or PAM, focuses on protecting accounts and permissions that can make sensitive or high-impact changes within an organization. Privileged identities may include system administrators, database administrators, cloud administrators, security teams, service accounts, and other identities with elevated access to critical infrastructure.
These accounts require stronger protection because attackers who compromise them may be able to disable security controls, create additional accounts, access confidential information, modify configurations, or disrupt business operations. Standard user protections may therefore be insufficient for privileged identities, especially when those accounts can affect large parts of the environment.
PAM solutions can introduce controls such as temporary elevation, approval workflows, credential protection, session monitoring, and detailed activity logging. Instead of giving administrators permanent access to everything, organizations can grant privileged permissions only when a legitimate task requires them and record what happens during the privileged session.
Privileged access management also supports accountability. Shared administrator accounts make it difficult to determine which individual performed a particular action. Assigning identifiable privileged accounts and maintaining detailed logs can improve investigations and auditing. As organizations strengthen IAM, privileged identities usually deserve some of the strongest authentication and monitoring controls available.
Multifactor Authentication and IAM Security
Multifactor authentication, commonly known as MFA, requires users to provide more than one type of evidence before gaining access. Instead of relying exclusively on a password, a system may require an additional authenticator such as a hardware security key, authenticator application, biometric factor, or another approved verification method.
MFA improves identity security because passwords can be stolen, guessed, reused, exposed through phishing, or leaked during breaches. When another factor is required, possession of a stolen password may not be sufficient to complete authentication. This provides an additional defensive layer around important accounts and applications.
Not every form of MFA offers the same resistance to attacks. Organizations increasingly need to consider phishing-resistant authentication methods for particularly sensitive systems and privileged users. Authentication should also be combined with device, session, behavioral, and risk signals where appropriate rather than assuming that successful MFA makes every future activity automatically trustworthy.
Organizations should make MFA adoption as practical as possible for legitimate users. Complicated authentication experiences can encourage workarounds or create unnecessary support requests. A well-designed IAM strategy balances security with usability by selecting authentication methods that provide meaningful protection without making normal access excessively difficult.
Single Sign-On and Federated Identity
Single Sign-On, usually abbreviated as SSO, allows users to authenticate once and then access multiple approved applications without repeatedly entering separate credentials. Organizations commonly use a centralized identity provider to authenticate employees and pass trusted identity information to connected applications.
SSO can improve productivity because employees no longer need to manage a different password for every business application. Centralization can also improve security administration because authentication policies can be enforced through a common identity platform. When an account is disabled centrally, access to connected applications can often be removed more efficiently.
Federated identity extends this concept by allowing separate organizations or systems to trust identity information provided by another identity provider. For example, an external business partner may use its own organization credentials to access an approved application without receiving an entirely separate local identity that must be manually maintained.
However, centralized identity also increases the importance of protecting the identity provider itself. If the primary authentication system is compromised, many connected applications may be affected. Organizations should therefore use strong authentication, secure administrative access, monitoring, recovery procedures, and carefully controlled configuration changes around their identity infrastructure.
IAM and Zero Trust Security
Zero Trust security is based on the idea that access should not automatically be trusted simply because a user or device is inside a traditional corporate network. Access decisions should instead evaluate identity, permissions, device condition, context, and other relevant signals. This makes identity and access management a central part of a Zero Trust security strategy.
In a Zero Trust environment, a user who successfully signs in may still face additional access checks before reaching sensitive information. The system could consider the user’s role, device security status, location, authentication strength, requested resource, and risk indicators before allowing or limiting access.
This approach is particularly valuable in cloud and remote-working environments because organizational resources may no longer sit behind a single network boundary. Employees may connect from different locations and devices while applications run across several cloud environments. Identity provides a consistent way to evaluate access even when network location is constantly changing.
Zero Trust does not mean that every employee is treated as suspicious. Instead, it means trust is not permanently assumed based on one successful login or network connection. Strong IAM allows organizations to continuously apply appropriate access policies while making legitimate access relatively seamless when risk remains low.
Conditional Access in Modern IAM
Conditional access enables organizations to make access decisions based on context rather than applying identical rules to every login attempt. Policies can evaluate signals such as user identity, device condition, application sensitivity, location, authentication method, risk indicators, and other environmental factors before granting access.
For example, a normal employee signing in from a managed company device may receive access with minimal friction. The same account attempting to access sensitive information from an unfamiliar device or unusual location may be required to complete stronger authentication or may be denied access entirely.
This risk-aware approach allows organizations to strengthen security without making every interaction equally restrictive. Low-risk activities can remain convenient, while higher-risk situations receive additional scrutiny. Conditional policies can therefore support both security and user experience when they are configured carefully.
Organizations should test policies before enforcing them broadly. Overly aggressive access rules can accidentally lock employees out of legitimate resources, while weak policies may provide little security improvement. Monitoring, staged deployment, emergency access planning, and regular policy review can help organizations implement conditional access more safely.
IAM for Cloud Security
Cloud computing has increased the importance of identity-based security because users and applications often interact directly with cloud resources through internet-accessible services and APIs. Access may no longer flow through a traditional office network, making identity and permissions essential controls for protecting cloud environments.
Cloud IAM systems allow administrators to define which identities can access specific resources and what actions they may perform. Permissions may apply to storage, databases, virtual machines, applications, administrative consoles, secrets, and other cloud services. Granular authorization can help organizations avoid giving users unnecessarily broad cloud access.
Misconfigured cloud permissions can create serious risk. An employee, service account, or application with excessive privileges may gain access to resources far beyond its intended purpose. Organizations should therefore review cloud roles, remove unused permissions, protect administrative identities, and maintain clear ownership of service accounts and automated identities.
Multi-cloud environments can make identity management even more complicated because businesses may use several providers alongside numerous SaaS applications. Central identity governance, federation, consistent authentication policies, and automated provisioning can help organizations maintain better visibility over access across these distributed environments.
Managing Non-Human and Machine Identities
Modern IAM increasingly needs to manage identities that do not belong to people. Applications, services, virtual machines, containers, automation workflows, APIs, and software agents may all need credentials or tokens to access other resources. These machine identities can become an important part of an organization’s attack surface.
Non-human identities are sometimes overlooked because they do not follow normal employee onboarding and offboarding processes. A service account created for a temporary project may remain active years after the project has ended. If the account holds broad permissions, attackers who discover its credentials could potentially access valuable resources.
Organizations should avoid sharing one identity across many applications whenever practical. Unique identities improve accountability because security teams can determine which service performed a particular action. Permissions can also be limited more precisely to the actual requirements of each workload rather than granting one shared account extensive access.
Credential management is equally important. Long-lived secrets stored in source code, configuration files, or insecure locations can become exposed. Organizations can reduce risk through secret management, short-lived credentials, workload identity technologies, access rotation, logging, and automated processes that remove unused identities when they are no longer required.
Identity Governance and Administration
Identity Governance and Administration, often shortened to IGA, focuses on ensuring that access remains appropriate throughout the identity lifecycle. While IAM systems control authentication and authorization, governance adds processes that help organizations understand who has access, why that access exists, and whether it should continue.
Access certification is a common governance activity. Managers or resource owners periodically review employee permissions and confirm whether those permissions are still necessary. These reviews can reveal outdated access that accumulated through role changes, temporary projects, departmental transfers, or forgotten system assignments.
Governance can also enforce approval workflows before sensitive access is granted. An employee requesting access to financial records, for example, may need approval from a manager or data owner. The organization can document who approved the access and why, providing greater accountability than informal permission changes.
Effective identity governance is especially valuable in large organizations where manually tracking thousands of permissions becomes unrealistic. Automated provisioning, policy enforcement, access reviews, reporting, and lifecycle integration can provide administrators with better visibility while reducing the administrative burden associated with managing access at scale.
Common Identity and Access Management Risks
Weak passwords remain a familiar identity risk, particularly when users reuse credentials across multiple services. Attackers can take advantage of exposed passwords, phishing campaigns, credential stuffing, and other techniques to gain access. Strong authentication practices reduce the dependence on passwords as the only barrier protecting accounts.
Excessive privileges create another major problem. Users may receive broader access than necessary because administrators want to avoid operational delays or because historical permissions are never removed. These privileges increase potential damage if an account is compromised or intentionally misused.
Orphaned accounts are another IAM weakness. Accounts belonging to former employees, contractors, applications, or abandoned services may remain active if offboarding processes fail. Attackers can potentially exploit these neglected identities because unusual activity may be less likely to attract immediate attention.
Poor visibility can make all these risks more difficult to detect. Organizations need to know which identities exist, which privileges they hold, where they authenticate, and how those privileges are being used. Centralized logging, identity inventories, access reviews, and security monitoring can help uncover suspicious or unnecessary access before it becomes a larger problem.
Benefits of Identity and Access Management
Improved cybersecurity is one of the most important benefits of IAM. Strong authentication, controlled permissions, least privilege, and regular access reviews reduce opportunities for unauthorized users to reach sensitive resources. Organizations can also respond more quickly when an account becomes compromised by disabling or restricting access centrally.
IAM can improve employee productivity as well. Employees need reliable access to applications and information to perform their responsibilities. Automated provisioning and single sign-on can reduce delays associated with requesting accounts, remembering numerous passwords, or waiting for administrators to configure basic access manually.
Another advantage is better visibility. Centralized identity systems can provide information about authentication activity, permission assignments, administrative changes, and access requests. Security teams can use this data to investigate suspicious behavior and understand how identities interact with critical systems.
IAM can also support compliance and auditing requirements by documenting how access is granted, reviewed, modified, and removed. While IAM alone does not guarantee compliance with any particular regulation, having structured identity governance makes it easier to demonstrate that organizations are actively controlling access to important information and systems.
Best Practices for Strong IAM Security
Organizations should begin by creating an accurate inventory of users, applications, service accounts, privileged accounts, and other identities. It is difficult to protect identities that administrators do not know exist. Ownership should also be assigned so someone remains responsible for reviewing each important account or application relationship.
Strong authentication should be required for sensitive access, particularly administrative accounts and externally accessible applications. Multifactor authentication can significantly strengthen account protection, while phishing-resistant methods may be appropriate for high-value environments. Shared accounts and weak default credentials should be minimized wherever possible.
Least privilege should become an ongoing process rather than a one-time configuration decision. Organizations should regularly review actual permission usage and remove access that users no longer require. Temporary elevation can be used when employees need powerful permissions only for specific administrative tasks.
Finally, identity events should be monitored alongside broader cybersecurity activity. Unusual sign-in locations, repeated authentication failures, unexpected privilege changes, dormant accounts becoming active, or abnormal access patterns may indicate suspicious behavior. Connecting identity monitoring with incident response helps security teams react quickly when unusual activity appears.
How Businesses Can Implement IAM Successfully
Successful IAM implementation begins with understanding business needs rather than immediately purchasing technology. Organizations should identify critical applications, sensitive information, high-risk users, existing authentication methods, and common access problems. This assessment helps determine which IAM capabilities should receive priority.
Many businesses benefit from beginning with foundational improvements such as centralized identity management, multifactor authentication, single sign-on, and automated employee provisioning. Once basic controls become consistent, organizations can introduce more advanced capabilities such as conditional access, identity governance, privileged access management, and risk-based authentication.
User experience should remain an important consideration throughout implementation. Security controls that are excessively complicated can generate support requests and encourage employees to search for workarounds. Clear onboarding, understandable authentication processes, and reliable self-service features can make strong identity security easier for employees to follow.
IAM should also be treated as an ongoing security program rather than a project that ends after deployment. Business applications change, employees move roles, new technologies appear, and attackers develop new techniques. Regular reviews, policy updates, employee education, security monitoring, and technology improvements are necessary to keep identity controls effective over time.
The Future of Identity and Access Management
Identity security is becoming increasingly important as organizations rely more heavily on cloud services, remote access, distributed applications, and automated workloads. Instead of protecting a single network boundary, businesses increasingly need to evaluate the identity behind every request and the context surrounding that request.
Authentication is also evolving beyond traditional passwords. Passkeys, hardware-backed credentials, biometric authentication, device-based trust, and other modern methods can reduce dependence on memorized secrets. Organizations will increasingly evaluate which methods provide the appropriate balance between usability, phishing resistance, recovery, and security.
Non-human identities are likely to receive even greater attention as automation and AI agents become more common. Intelligent software may interact with business systems, access APIs, retrieve information, and perform tasks on behalf of users. Organizations will need to ensure these agents have identifiable, limited, auditable permissions instead of broad shared credentials.
Ultimately, the future of IAM will involve more continuous and context-aware access decisions. Identity, device state, behavior, risk, privilege level, and resource sensitivity can all contribute to whether access is permitted. Organizations that build strong identity foundations today will be better positioned to secure increasingly complex digital environments.
Final Thoughts
Identity and Access Management is one of the foundations of modern cybersecurity because almost every digital interaction begins with an identity requesting access to something. IAM provides the processes and technologies needed to verify those identities, assign appropriate permissions, and remove access when it is no longer necessary.
A strong IAM strategy combines authentication, authorization, multifactor authentication, single sign-on, role-based access control, identity governance, privileged access management, and lifecycle management. These controls work together to limit unauthorized access while helping legitimate employees, customers, and applications use the resources they actually need.
Businesses should pay particular attention to least privilege and identity lifecycle management. Permissions should not remain permanent simply because they were once required. Regular access reviews, automated deprovisioning, strong authentication, and monitoring can significantly reduce the number of unnecessary pathways into sensitive systems.
As cloud computing, remote work, automation, and AI continue expanding the number of digital identities organizations must protect, IAM will remain a central cybersecurity priority. Organizations that understand who has access, why they have it, and how that access is being used can build stronger and more manageable security environments.
Frequently Asked Questions
What is IAM in cybersecurity?
Identity and Access Management is a cybersecurity framework for managing digital identities and controlling access to systems, applications, data, and other resources. It helps ensure that authorized identities receive appropriate permissions.
What are the main components of IAM?
The main components include identity management, authentication, authorization, access control, identity lifecycle management, governance, single sign-on, multifactor authentication, and privileged access management.
What is the difference between IAM and authentication?
Authentication verifies that a user or system is who it claims to be, while IAM covers the broader process of managing identities, authentication, permissions, governance, and access throughout their lifecycle.
Why is IAM important for cloud security?
Cloud resources can be accessed from many locations and services, making identity-based controls essential. IAM helps organizations restrict cloud permissions, protect administrative access, and apply least privilege to users and workloads.
How does IAM support Zero Trust security?
IAM supports Zero Trust by continuously verifying identities and controlling access according to permissions, authentication strength, device information, risk, and context instead of automatically trusting users based on network location.