
Traditional cybersecurity often worked on a simple assumption: people and devices inside a company network could be trusted more than those outside it. That approach made sense when employees worked mainly from offices and important systems stayed behind a company firewall. Today, cloud applications, remote work, mobile devices, contractors, and distributed teams have made that security model much harder to maintain.
Zero Trust security takes a different approach. Instead of automatically trusting someone because they are already inside a network, it continuously verifies users, devices, applications, and access requests. The basic idea is simple: trust should be earned through verification, and every person or system should receive only the access needed to complete a legitimate task.
What Is Zero Trust Security?
Zero Trust security is a cybersecurity model based on the principle of never automatically trusting a user, device, or connection simply because it is inside an organization’s network. Every access request is evaluated according to factors such as identity, device health, location, behavior, and the sensitivity of the resource being requested.
This approach is often summarized as “never trust, always verify.” The phrase does not mean employees are treated as suspicious people. Instead, it means security decisions should rely on evidence rather than assumptions, helping organizations reduce the damage caused by stolen passwords, compromised devices, malicious software, or unauthorized users.
Zero Trust is not one product that can be purchased and installed overnight. It is a security strategy that combines identity management, access controls, device security, network segmentation, monitoring, and strong authentication. Companies usually adopt it gradually by improving how they verify users and limit access to important systems.
Why Traditional Network Security Is No Longer Enough
Older security models often focused on building a strong perimeter around the company network. Firewalls and other controls protected the boundary, while users and devices inside that boundary were given greater freedom. This approach becomes risky when an attacker successfully enters the network because internal access may allow movement toward other systems.
Modern organizations also operate far beyond one physical office. Employees may work from home, use cloud software, connect through mobile devices, or collaborate with external contractors. Important applications and data can live across several cloud platforms, making it difficult to define one secure network perimeter that separates everything trusted from everything untrusted.
Attackers also frequently use stolen credentials rather than attempting to break directly through a firewall. If a criminal obtains an employee password, a traditional system may treat the login as legitimate. Zero Trust reduces this risk by checking additional conditions and limiting what the account can access even after authentication succeeds.
The Core Principles of Zero Trust
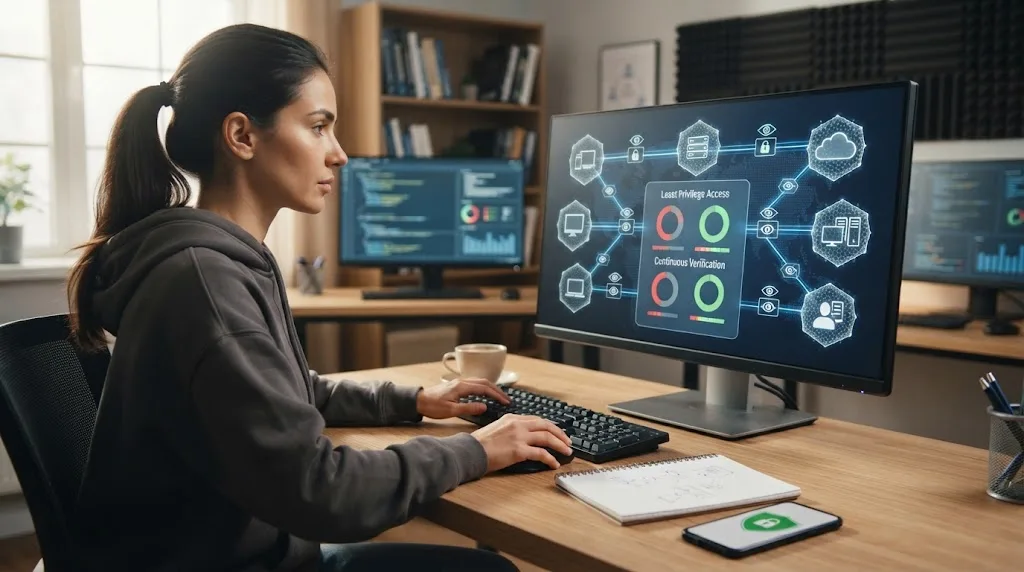
The first principle is continuous verification. A user who successfully signs in once should not automatically receive unrestricted access for an entire day or session. Security systems can continually evaluate identity, device status, location, unusual behavior, and other risk signals before allowing access to sensitive resources or important business applications.
The second principle is least-privilege access. Employees should receive only the permissions necessary to perform their jobs rather than broad access to every system. A marketing employee, for example, may need access to analytics and content platforms but not financial databases or engineering infrastructure unrelated to their responsibilities.
The third principle assumes that a breach can happen. Instead of designing security as though attackers will always remain outside, Zero Trust limits how far they can move if one account or device becomes compromised. Segmentation, monitoring, restricted permissions, and strong identity controls can reduce the impact of an individual security incident.
How Zero Trust Security Works
When someone attempts to access an application or file, a Zero Trust system evaluates the request before granting permission. It may check the user’s identity, authentication method, device condition, geographic location, connection type, recent activity, and the sensitivity of the requested information. Access is granted only when the request meets established security policies.
Imagine an employee usually signs into a work application from a managed laptop in one country. If the same account suddenly attempts to connect from an unknown device in another location, the system may require additional verification or block access. This risk-based approach helps organizations respond to suspicious behavior without treating every normal activity as an attack.
Access decisions can also change during a session. A user may be allowed to view a low-risk document but need stronger authentication before opening confidential financial information. Zero Trust therefore treats security as an ongoing process rather than a single login check performed when someone first connects to the network.
Identity Verification Is Central to Zero Trust
Strong identity management is one of the foundations of Zero Trust security. Organizations need to know who is requesting access before deciding what that person should be allowed to do. Usernames and passwords alone are often insufficient because passwords can be stolen through phishing, credential leaks, malware, or password reuse.
Multifactor authentication adds another layer by requiring additional proof of identity. Depending on the organization, this may involve an authenticator app, security key, device confirmation, biometric factor, or another approved method. If an attacker steals a password, the second factor can make unauthorized account access considerably more difficult.
Identity systems can also evaluate behavior over time. Unusual login times, impossible travel patterns, repeated failed attempts, or unexpected access to sensitive applications may trigger stronger verification. This adaptive approach allows security teams to focus additional controls on higher-risk situations without creating the same level of friction for every routine login.
Device Security Also Matters
Zero Trust does not evaluate only the person requesting access. The condition of the device can be equally important because a legitimate employee using a compromised laptop may still create a serious security risk. Organizations can check whether devices are managed, updated, encrypted, protected by security software, and compliant with company policies.
An outdated computer missing important security patches may receive limited access until required updates are installed. Similarly, an unknown personal device might be prevented from downloading confidential files even when the user has valid credentials. These controls reduce the possibility that sensitive information will be exposed through insecure or unmanaged endpoints.
Browser security also contributes to safer endpoint use. Employees should keep browsers updated, avoid suspicious extensions, and use tools that reduce unnecessary tracking and exposure. People interested in additional browsing protection can also explore privacy browsers as part of a broader approach to safer web activity.
Least-Privilege Access Reduces Security Risk
Least privilege means giving people and systems only the access they genuinely need. Instead of granting employees wide permissions because they might need them someday, organizations assign access according to specific roles and responsibilities. Removing unnecessary privileges reduces the number of sensitive resources an attacker could reach through one compromised account.
Permissions should also change when job responsibilities change. An employee who moves from finance to marketing may no longer need access to certain accounting systems. Regular access reviews help remove outdated privileges and prevent organizations from accumulating excessive permissions that remain active long after the original business need disappears.
Temporary access can also support Zero Trust principles. An administrator might receive elevated permissions only when performing a specific maintenance task and lose them afterward. This approach reduces the time powerful accounts remain available, helping limit the opportunities attackers have to misuse highly privileged credentials if those accounts become compromised.
Network Segmentation Limits Attacker Movement
Network segmentation divides systems into smaller controlled areas instead of allowing every device to communicate freely with everything else. In a Zero Trust environment, sensitive databases, employee devices, guest networks, development systems, and business applications may be separated according to their purpose and security requirements.
This separation becomes especially valuable after a compromise. If an attacker gains access to one employee laptop, segmentation can prevent that device from immediately reaching every server or application in the organization. The attacker must overcome additional security controls before moving from one protected area to another.
Microsegmentation takes this idea further by applying very detailed security policies between individual workloads, applications, or services. Organizations can control exactly which systems are allowed to communicate and under what circumstances. These restrictions reduce unnecessary network exposure and make lateral movement considerably more difficult during a security incident.
Continuous Monitoring Helps Detect Suspicious Activity
Zero Trust depends on visibility because organizations cannot verify activity they cannot see. Security systems collect information about logins, devices, access requests, application activity, and unusual behavior. This information helps identify patterns that may suggest credential theft, malware, insider misuse, or attempts to reach systems outside a user’s normal responsibilities.
Monitoring does not mean every activity automatically triggers an alarm. Effective systems use context to distinguish normal behavior from higher-risk events. An employee accessing the same application from a known device every morning presents a different risk level from the same account suddenly downloading thousands of sensitive files from an unfamiliar location.
Security teams can use these signals to respond more quickly. Suspicious sessions may be blocked, authentication can be required again, and compromised accounts can be disabled before further damage occurs. Continuous monitoring therefore complements prevention by helping organizations identify threats that successfully bypass an earlier layer of defense.
Zero Trust and Remote Work
Remote work is one reason Zero Trust has become increasingly important. Employees may connect from home networks, coworking spaces, hotels, or mobile hotspots rather than company-controlled offices. Automatically trusting connections simply because someone knows the correct password is no longer sufficient when devices and users can appear from almost anywhere.
Zero Trust allows organizations to focus on identity and device health instead of physical location. A properly verified employee using a managed, secure laptop can access approved applications without needing to be inside the office. At the same time, unfamiliar devices or risky login attempts can receive stricter controls regardless of where they originate.
This model can also improve the experience of legitimate remote workers. Instead of giving employees broad network access through traditional methods, organizations can provide direct access only to the applications they need. Limiting unnecessary connections reduces exposure while allowing users to reach approved resources from different locations more securely.
Benefits of Zero Trust Security
One major benefit is reduced exposure when an account becomes compromised. Because access is limited according to identity, device, and business need, stealing one employee password does not necessarily provide access to the entire environment. Attackers encounter additional verification requirements and restrictions as they attempt to reach more sensitive resources.
Zero Trust can also improve visibility into who is accessing important information. Organizations gain a clearer understanding of which users, devices, and applications interact with different systems. Better visibility supports incident response, access reviews, compliance efforts, and investigations when unusual behavior needs to be understood quickly.
Another advantage is that Zero Trust can support modern technology environments. Businesses increasingly use cloud services, software-as-a-service applications, mobile devices, remote workers, and third-party contractors. A security model centered on identities and access policies can adapt more easily to these environments than one that depends entirely on a traditional office network boundary.
Challenges of Implementing Zero Trust
Moving to Zero Trust can be complicated because organizations often have years of existing systems, permissions, and network configurations. Some older applications may not support modern authentication methods or detailed access controls. Security teams first need to understand which users, devices, applications, and data exist before they can design effective policies.
Poor implementation can also frustrate employees. Constant authentication prompts, blocked applications, or restrictive rules may encourage users to search for workarounds. Successful Zero Trust programs therefore balance strong security with usability by applying additional verification when risk is higher instead of creating unnecessary obstacles during every routine activity.
Zero Trust also requires ongoing maintenance rather than a one-time project. Roles change, devices are replaced, applications move to the cloud, and new threats appear. Organizations need regular access reviews, policy updates, monitoring, user training, and technical improvements to ensure the security model continues reflecting how the business actually operates.
How Organizations Can Start Using Zero Trust
A practical starting point is identifying critical systems, sensitive information, users, and devices. Organizations should understand what they are trying to protect before adding new security technology. Mapping access relationships can reveal where excessive permissions, unmanaged devices, shared accounts, or unnecessary network connections create avoidable risk.
The next step is strengthening identity controls. Enabling multifactor authentication, removing unused accounts, creating role-based permissions, and reducing administrator access can provide meaningful improvements quickly. Organizations can then introduce device checks, segmentation, monitoring, and more detailed access policies as their Zero Trust program becomes more mature.
Implementation does not need to happen everywhere at once. Many organizations begin with high-value applications or sensitive departments and expand gradually based on lessons learned. This phased approach makes the transition easier to manage while still improving security in areas where compromised accounts or devices would create the greatest potential damage.
Conclusion
Zero Trust security replaces automatic trust with continuous verification. Instead of assuming users and devices are safe because they are already inside a network, organizations evaluate each access request according to identity, device health, context, and business need. This approach is better suited to modern environments where employees and applications operate across offices, homes, mobile devices, and cloud platforms.
Its main principles include strong identity verification, least-privilege access, device security, segmentation, and continuous monitoring. These layers help reduce the damage caused by stolen credentials or compromised devices. Even when an attacker gets through one defense, additional controls can prevent unrestricted movement across the organization.
Zero Trust is not a single product or instant security solution. It is an ongoing strategy that requires clear policies, reliable technology, regular access reviews, and cooperation between security teams and employees. When implemented thoughtfully, it can provide stronger protection without preventing legitimate users from reaching the resources they need.
FAQs
What does Zero Trust mean in simple terms?
Zero Trust means no user or device receives automatic access simply because it is already inside a network. Every request is verified, and users receive only the permissions necessary for legitimate work.
Is Zero Trust the same as a firewall?
No. A firewall is one security technology that controls network traffic, while Zero Trust is a broader strategy involving identity verification, device security, access controls, segmentation, monitoring, and other protective measures.
Does Zero Trust mean employees are not trusted?
No. Zero Trust focuses on verifying digital access rather than questioning employee character. The model assumes accounts and devices can become compromised, so security decisions rely on evidence instead of location or previous access.
Do small businesses need Zero Trust security?
Small businesses can benefit from Zero Trust principles such as multifactor authentication, limited permissions, secure devices, and regular account reviews. They do not necessarily need complex enterprise systems to begin applying the approach.
Can Zero Trust prevent every cyberattack?
No security model can prevent every attack. Zero Trust reduces risk by making unauthorized access and lateral movement more difficult, but organizations still need updates, backups, malware protection, phishing defenses, and employee security awareness.