
CAPTCHA Acronym: What It Means and How CAPTCHA Works
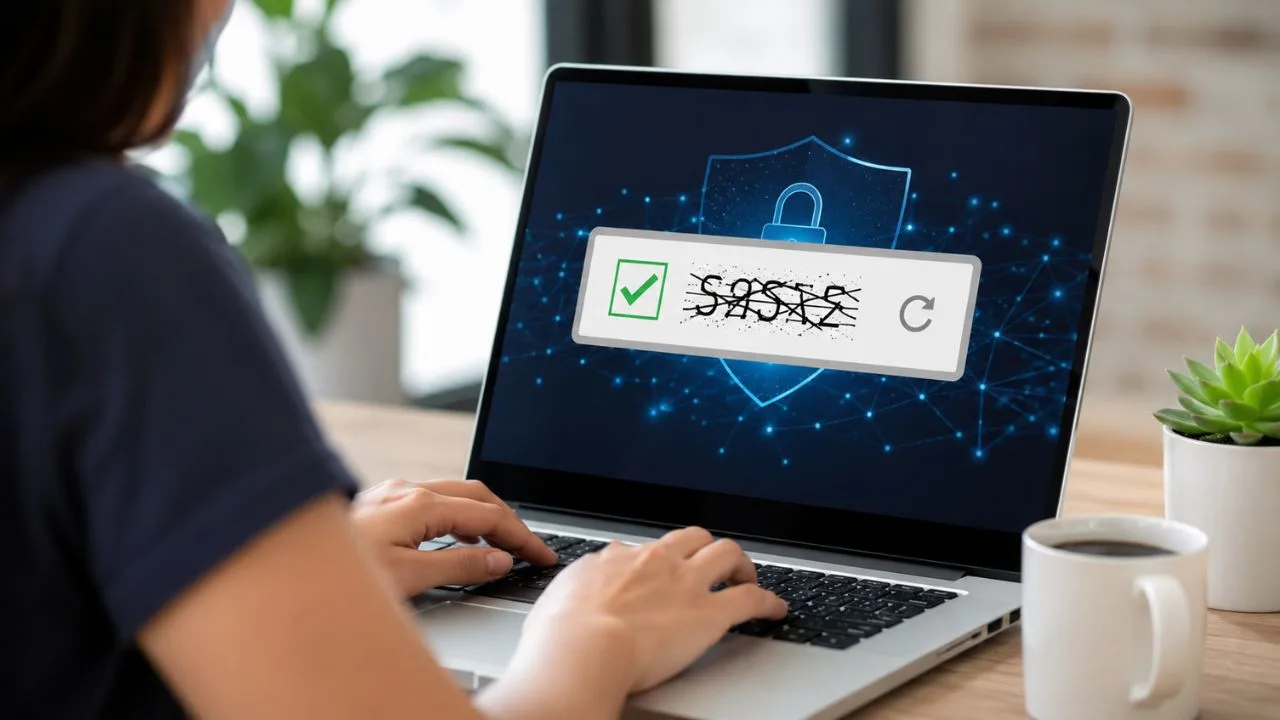
You have probably encountered a CAPTCHA while logging into an account, submitting a form or making an online purchase. It may ask you to select traffic lights, type distorted letters or simply check a box. These small tests help websites decide whether a visitor is a real person or an automated computer program.
The CAPTCHA acronym stands for Completely Automated Public Turing test to tell Computers and Humans Apart. Although the full form sounds complicated, its purpose is simple: create a challenge that most humans can complete but automated bots are expected to find difficult. The result helps websites control suspicious or unwanted automated activity.
Traditional CAPTCHA tests relied heavily on distorted text, numbers and image-recognition puzzles. Modern systems can also examine technical and behavioral signals before deciding whether a visitor needs to complete a visible challenge. This approach can reduce interruptions for legitimate users while maintaining protection against spam, fake registrations and automated attacks.
However, CAPTCHA technology is not perfect. Artificial intelligence can now solve many challenges that were once difficult for machines, while some legitimate users struggle with visual, audio or cognitive tests. Understanding the CAPTCHA meaning, benefits and limitations can help both internet users and website owners make better security decisions.
What Does CAPTCHA Stand For?
CAPTCHA stands for Completely Automated Public Turing test to tell Computers and Humans Apart. The phrase describes a security test that is created, presented and evaluated automatically by a computer. A person does not normally need to review every answer because the system determines whether the response meets its verification requirements.
The words “Public Turing test” connect the CAPTCHA definition to ideas introduced by computer scientist Alan Turing. A traditional Turing test explores whether a machine can behave in a way that appears human. A CAPTCHA reverses that general idea by asking a computer system to determine whether the participant is likely to be human.
The term CAPTCHA was introduced by researchers at Carnegie Mellon University around 2000. Early CAPTCHA technology focused on tasks that people could perform relatively easily but computer programs could not reliably complete. Distorted text recognition became one of the most familiar examples because older optical character recognition systems struggled with irregular letters.
The CAPTCHA full form is sometimes written incorrectly as “Completely Automatic Public Turing Test.” However, the widely accepted wording uses automated, not automatic. Searches for CAPTCHA abbreviation, CAPTCHA acronym and CAPTCHA meaning generally refer to the same human-verification technology used to separate legitimate website visitors from automated software.
Breaking Down the CAPTCHA Acronym
The word completely means the test operates without routine human supervision. A website automatically generates or displays the challenge, receives the visitor’s response and evaluates the result. This automation allows CAPTCHA systems to process thousands or millions of website interactions without requiring staff members to examine every login, registration or form submission.
The word automated refers to the way the technology performs its security checks. The system can select a challenge, monitor available browser signals and return a verification result. Automation makes CAPTCHA suitable for high-traffic websites where manually checking whether every visitor is a person would be expensive, slow and unrealistic.
The phrase public Turing test indicates that the general method is publicly available rather than hidden from users. People and software developers can understand the type of challenge being presented. The security does not depend entirely on keeping the test secret; it depends on making the challenge more difficult for automated systems than for genuine users.
The final phrase, to tell computers and humans apart, explains the main goal. CAPTCHA technology attempts to separate human activity from bot activity by examining a response or interaction. It does not prove a person’s identity, confirm that the person is trustworthy or replace account security measures such as passwords and multifactor authentication.
Why Do Websites Use CAPTCHA Tests?
Websites commonly use CAPTCHA tests to reduce automated spam. Without human verification, bots may submit advertising links, misleading messages or harmful content through contact forms and comment sections. A CAPTCHA code adds friction to automated submissions, making it more difficult and costly for spammers to send large numbers of unwanted messages.
CAPTCHA verification can also limit fake account creation. Automated programs may register thousands of accounts for scams, referral abuse, content manipulation or fraudulent promotions. Requiring a CAPTCHA during registration helps websites slow down mass sign-ups and focus additional security checks on visitors whose behavior appears unusual or potentially risky.
Login pages sometimes use CAPTCHA protection to discourage credential-stuffing and brute-force attacks. In these attacks, bots repeatedly test stolen or guessed usernames and passwords. A human-verification challenge can reduce the speed of automated attempts, although it should always be combined with rate limiting, secure authentication and suspicious-login detection.
Online stores, ticketing platforms and polling systems may also use bot detection to protect limited resources. Automated buyers can attempt to purchase large quantities of products before genuine customers have a fair opportunity. CAPTCHA security helps control this activity, but sophisticated bot management usually requires several protections working together rather than one challenge alone.
How Does a CAPTCHA Work?
A basic CAPTCHA presents a challenge that is expected to be easier for humans than for automated software. The challenge might display distorted characters, play an audio recording or show several photographs. The visitor provides an answer, and the website checks whether it matches the response stored or expected by the CAPTCHA system.
Some CAPTCHA tests use a challenge-response process. The server creates a temporary challenge and sends it to the visitor’s browser. After the visitor completes the task, the CAPTCHA provider returns a token or verification result. The website must then validate that result on the server before accepting the form, login or transaction.
Modern CAPTCHA systems may perform risk analysis before showing a visible puzzle. They can evaluate signals related to the browser session, request patterns and interaction behavior. When the activity appears normal, the visitor may pass without completing a difficult task. Suspicious activity may trigger an image challenge or additional verification step.
A successful CAPTCHA result does not necessarily prove that the visitor is human with absolute certainty. It indicates that the interaction met the system’s verification threshold. Bots can sometimes solve challenges, while legitimate users may fail them. For this reason, CAPTCHA should function as one part of a broader website security strategy.
Common Types of CAPTCHA
A text CAPTCHA asks the user to recognize letters or numbers displayed in a distorted image. Lines, noise, unusual fonts and overlapping characters may be added to confuse optical character recognition software. Although this type became widely recognized, it can frustrate users when the text is difficult to read or visually ambiguous.
An image CAPTCHA asks the visitor to select pictures containing a particular object, such as bicycles, crosswalks or buses. Image-recognition challenges can feel more intuitive than distorted text, but unclear image boundaries may create confusion. Advances in computer vision have also made many visual tasks increasingly manageable for artificial intelligence systems.
An audio CAPTCHA reads numbers, words or sounds that the visitor must identify and enter. It is often offered as an alternative for users who cannot complete a visual challenge. Background noise may be added to discourage automated speech recognition, although that noise can also make the recording difficult for some human listeners to understand.
Invisible and risk-based CAPTCHA systems attempt to verify visitors with minimal interaction. Instead of presenting every person with a puzzle, the system evaluates available signals and only challenges higher-risk sessions. Other CAPTCHA alternatives use lightweight browser checks, proof-of-work methods or private access tokens to reduce dependence on traditional image-selection tasks.
CAPTCHA vs reCAPTCHA: What Is the Difference?
CAPTCHA is the general name for any automated test designed to distinguish humans from computer programs. It can describe text puzzles, image challenges, audio tests, mathematical questions and newer risk-based verification methods. Different companies and open-source projects can create CAPTCHA technologies using their own approaches and security models.
reCAPTCHA is a specific CAPTCHA service developed from a Carnegie Mellon research project and later acquired by Google. Earlier versions used distorted words and helped digitize text from scanned books. Later versions introduced the familiar “I’m not a robot” checkbox, image-selection challenges and background risk analysis.
The reCAPTCHA checkbox does not rely only on whether a person clicks the box correctly. The service may analyze information associated with the interaction to estimate whether the activity appears legitimate. Depending on the risk assessment, a visitor may pass immediately or receive an additional visual or audio challenge.
Therefore, CAPTCHA and reCAPTCHA are not interchangeable terms. CAPTCHA is the broad category, while reCAPTCHA is one product within that category. Other human-verification and bot-protection tools include hCaptcha, Cloudflare Turnstile and custom systems developed for particular websites, applications or security environments.
Are CAPTCHAs Still Effective Against Bots?
CAPTCHA tests can still reduce basic automated abuse, especially when bots are programmed to submit forms without interpreting page content. A simple challenge may block low-effort scripts and reduce spam volume. This makes CAPTCHA useful for contact forms, account registrations and other areas frequently targeted by unsophisticated automation.
However, CAPTCHA technology is involved in a continuing competition between security providers and bot developers. Improvements in machine learning, speech recognition and computer vision have made traditional puzzles easier for software to solve. Attackers may also use human-solving services, compromised browsers or automated systems trained for specific challenge formats.
A CAPTCHA can become less effective when it is predictable or incorrectly implemented. For example, attackers may bypass a challenge if the website trusts a client-side result without validating it on the server. Reusable verification tokens, exposed secret keys and weak rate controls can also undermine an otherwise reliable CAPTCHA integration.
The strongest approach is layered bot protection. CAPTCHA should work alongside rate limiting, server-side validation, account monitoring, device or session analysis and secure authentication. Website owners should also protect application programming interfaces because attackers may avoid the visible webpage and send automated requests directly to an unprotected endpoint.
CAPTCHA Accessibility Challenges
Visual CAPTCHA tests can create barriers for people who are blind, have low vision or experience difficulty recognizing distorted characters. Image-selection puzzles may also be challenging when the pictures are small, low contrast or culturally unclear. Making a puzzle harder for software can unintentionally make it harder for legitimate human visitors.
Audio CAPTCHA provides an alternative for some users, but it does not solve every accessibility problem. People who are deaf or hard of hearing may be unable to use it, while background noise can make spoken characters difficult to understand. Users with cognitive, language or attention-related disabilities may also struggle with complex instructions.
An accessible CAPTCHA implementation should provide more than one verification method. Instructions need to be clear, controls should work with keyboards and screen readers, and users should have enough time to complete the task. Error messages should explain what happened without forcing the person to restart an unnecessarily long process.
Website owners can also consider challenge-free alternatives that evaluate risk without requiring every visitor to solve a puzzle. Reducing visible tests can improve accessibility and conversion rates, but alternative systems must still be carefully assessed. Security, usability, privacy and accessibility should be evaluated together rather than treated as separate concerns.
CAPTCHA Privacy and User Experience Concerns
Some modern CAPTCHA services analyze information beyond the answer entered by the visitor. Depending on the provider and configuration, the system may evaluate browser, device, network or interaction signals. These checks can improve bot detection, but website owners should understand what information is processed and how the provider handles it.
Privacy requirements may vary according to the website’s audience, location and legal obligations. Businesses should review the CAPTCHA provider’s documentation, contractual terms and data-processing practices before implementation. A tool should not be selected only because it is popular or easy to install, especially when forms collect sensitive customer information.
Poor CAPTCHA placement can also damage the user experience. A difficult challenge presented at the end of a long form may cause visitors to abandon their submission. Repeated puzzles, unclear images, expired tokens and unexplained errors can be particularly frustrating for users trying to complete a purchase or access an important account.
Website owners should measure whether CAPTCHA protection solves a genuine abuse problem. A low-risk form may benefit more from hidden fields, rate controls and server-side spam filtering. Visible challenges can then be reserved for suspicious activity instead of making every visitor prove they are human regardless of their behavior.
Why CAPTCHA Tests Sometimes Fail
A CAPTCHA may fail because JavaScript is disabled, blocked or unable to load correctly. Browser privacy extensions, content blockers, corporate firewalls and unstable internet connections can interfere with the required scripts. Refreshing the page, checking the connection or temporarily adjusting an extension may allow the verification tool to load properly.
Challenges can also expire when a form remains open for too long. CAPTCHA tokens are commonly temporary because permanent or reusable tokens would create security risks. When a verification result expires, the user may need to complete a new challenge before submitting the form again.
A shared network or virtual private network can sometimes trigger additional checks. Many visitors may appear to use the same internet address, or the address may have a history of suspicious automated traffic. Switching to a trusted network may help, but users should not weaken important privacy protections merely to avoid a challenge.
Repeated failure may also result from incorrect website configuration rather than user behavior. The site may be using invalid keys, an unsupported domain or incomplete server-side verification. When many visitors report the same problem, the website owner should test the integration instead of assuming that every failed attempt comes from a bot.
How to Complete a CAPTCHA Successfully
Read the instructions before selecting images or entering a CAPTCHA code. Some challenges ask for every square containing part of an object, while others expect only complete objects. Moving too quickly can lead to missed tiles, incorrect characters and repeated challenges that take longer than completing the first test carefully.
When distorted text is unreadable, use the refresh option to request another challenge. Avoid repeatedly guessing because several incorrect attempts may make the system more cautious. An audio option may be helpful when the visual test remains unclear, provided that the recording is understandable and accessible to you.
Make sure browser scripts and cookies required by the website are not completely blocked. Updating an outdated browser can also resolve compatibility problems. However, avoid installing unknown software or suspicious browser extensions that claim to bypass CAPTCHA tests, because such tools may collect personal information or expose the device to security risks.
When a CAPTCHA continues to loop, clear the affected site’s temporary data or try a private browser window. A different trusted network may also help when the current internet address is being treated as high risk. If the issue affects only one website, report the problem to that site’s support team.
CAPTCHA Best Practices for Website Owners
Place CAPTCHA protection only where automated abuse creates a meaningful risk. Common locations include registration pages, login recovery forms, comment areas and high-value transactions. Adding a challenge to every page can slow down legitimate visitors without delivering a proportional security benefit.
Use risk-based verification whenever appropriate. Low-risk users should be able to proceed with little or no interruption, while suspicious sessions can receive stronger challenges. This adaptive approach protects important actions while reducing unnecessary friction for customers, subscribers and other legitimate website visitors.
Always validate CAPTCHA tokens on the server. Client-side confirmation alone can be modified or bypassed by an attacker. Verification tokens should be checked for authenticity, expiration, expected domain or application context and reuse before the protected action is accepted.
Combine CAPTCHA with other security controls. Rate limiting can reduce repeated attempts, while honeypot fields can catch simple form bots without affecting real users. Logging, fraud analysis, secure authentication and API protection help identify attacks that a standalone human-verification challenge might miss.
Modern CAPTCHA Alternatives
Cloudflare Turnstile is an example of a CAPTCHA alternative designed to reduce visible challenges. It can evaluate browser-based signals and present visitors with a simpler verification process. The service can be embedded on websites even when their traffic is not routed through Cloudflare’s wider network.
Private access tokens and device-attestation methods can sometimes confirm that a request comes from a legitimate device without exposing the same level of identifying information. These approaches may improve privacy and reduce user effort, although availability depends on the visitor’s browser, device and operating system.
Honeypot fields are hidden form inputs that normal visitors should leave empty. Basic bots may fill every available field, allowing the website to reject the submission. Honeypots are easy to use and cause little friction, but advanced bots can recognize them, so they should not be the only protection for sensitive actions.
Behavioral analysis, rate limiting and email verification can also reduce automated abuse. Each method addresses a different part of the problem, and none is universally effective by itself. The best CAPTCHA alternative depends on the website’s traffic, risk level, privacy requirements, technical resources and accessibility goals.
The Future of CAPTCHA Technology
Traditional distorted-text puzzles are becoming less practical as artificial intelligence improves. Tasks that once separated humans from computers may no longer provide a reliable distinction. Increasing the difficulty can also harm genuine users before it creates a meaningful barrier for sophisticated automated systems.
Future bot detection is likely to focus more on context and risk than isolated puzzles. A system can evaluate whether an interaction matches normal behavior and request additional verification only when the risk is elevated. This approach can make everyday browsing smoother while preserving stronger protection for sensitive actions.
Privacy-preserving verification will also become increasingly important. Users and regulators expect organizations to limit unnecessary data collection, while website owners still need protection from fraud and abuse. Verification methods that produce a trustworthy result without revealing excessive personal information may become more widely adopted.
CAPTCHA may therefore evolve rather than disappear. The recognizable image grid or distorted word could become less common, while invisible and adaptive verification continues performing a similar function. The central purpose of the CAPTCHA acronym—telling computers and humans apart—remains relevant even as the methods used to achieve it change.
Final Thoughts on the CAPTCHA Acronym
The CAPTCHA acronym means Completely Automated Public Turing test to tell Computers and Humans Apart. It describes a human-verification method used to reduce spam, fake accounts, automated login attempts and other bot-driven activity. CAPTCHA is the general technology category, while reCAPTCHA is one well-known service within it.
CAPTCHA tests have changed considerably since the early distorted-text puzzles. Image challenges, audio options, checkboxes and invisible risk assessments now offer different ways to evaluate website interactions. Newer CAPTCHA alternatives aim to protect forms and accounts without forcing every legitimate visitor to complete a frustrating task.
Despite its value, CAPTCHA is not a complete security solution. Automated systems may solve or bypass challenges, and inaccessible designs can block real users. Effective protection requires server-side verification, rate limiting, secure authentication, bot monitoring and careful attention to privacy and accessibility.
For website visitors, CAPTCHA is usually a brief checkpoint designed to protect an online service. For website owners, it is one tool within a larger security system. The best implementation creates enough resistance to discourage bots while allowing genuine people to complete their intended actions with minimal difficulty.
Frequently Asked Questions
What is the full form of CAPTCHA?
CAPTCHA stands for Completely Automated Public Turing test to tell Computers and Humans Apart. It is an automated security check designed to distinguish human users from bots.
Why do websites ask me to complete a CAPTCHA?
Websites use CAPTCHA verification to reduce spam, fake registrations, automated login attempts and fraudulent activity. The test adds a security barrier before a form or action is accepted.
Is CAPTCHA the same as reCAPTCHA?
No. CAPTCHA is the general name for human-verification tests, while reCAPTCHA is a specific CAPTCHA service associated with Google. Other providers offer similar bot-detection technologies.
Can bots solve CAPTCHA tests?
Some advanced bots and artificial intelligence systems can solve or bypass certain CAPTCHA challenges. That is why websites should combine CAPTCHA with rate limiting, authentication security and server-side bot detection.
Why does CAPTCHA keep appearing repeatedly?
Repeated challenges may be triggered by unusual traffic, a shared network, a VPN, blocked browser scripts or incorrect answers. Website configuration problems can also cause CAPTCHA loops for legitimate visitors.