
Eavesdropping in Cybersecurity: Risks & Prevention
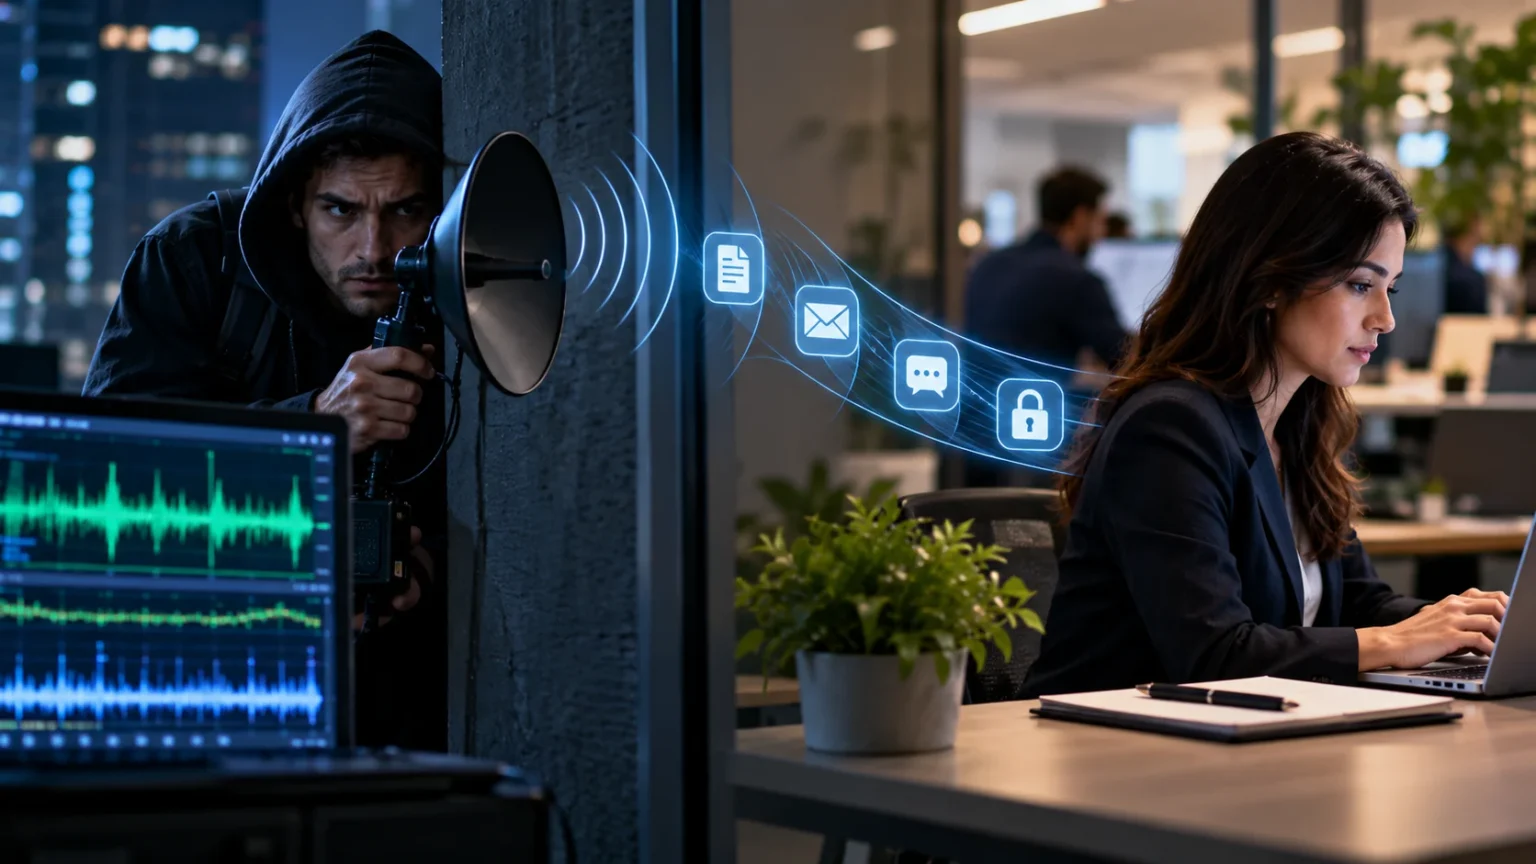
Eavesdropping in cybersecurity occurs when an unauthorized person secretly intercepts, listens to, or collects information being transmitted between people, devices, applications, or networks. Instead of physically overhearing a conversation, a cyber eavesdropper may target network traffic, wireless communications, login sessions, emails, voice calls, or other digital information. The attacker’s goal is often to obtain passwords, financial information, business data, personal messages, or authentication details without being noticed. Some attacks simply observe traffic, while others manipulate communications so information passes through attacker-controlled systems. Strong encryption and secure network practices have made many traditional interception techniques more difficult, but eavesdropping remains an important security risk. Understanding how these attacks happen is therefore essential for protecting modern digital communications.
Eavesdropping attacks can affect individuals, businesses, government organizations, healthcare systems, and virtually any environment where sensitive information travels electronically. Public Wi-Fi, poorly configured networks, outdated security protocols, compromised routers, and insecure applications can all create opportunities for data interception. Attackers may also combine eavesdropping with phishing, malware, stolen credentials, or man-in-the-middle techniques to gather more valuable information. Fortunately, many practical defenses can significantly reduce exposure, including HTTPS, modern Wi-Fi security, virtual private networks, multifactor authentication, secure configuration, and continuous monitoring. Effective cybersecurity does not depend on one defensive tool alone. It requires multiple layers that protect information while it is stored, processed, and transmitted.
What Is Eavesdropping in Cybersecurity?
Eavesdropping in cybersecurity is the unauthorized interception of digital communications as information moves between devices or systems. The term can refer to monitoring network packets, capturing wireless transmissions, observing unencrypted conversations, or secretly obtaining data exchanged between users and online services. A person might think of data traveling directly from a laptop to a website, but communication often passes through routers, wireless access points, internet providers, gateways, and other infrastructure. If one of those communication points is compromised or insecure, sensitive information may become exposed. The attacker may not need to alter the data at all. Simply collecting readable information can provide enough intelligence for fraud, account compromise, or further attacks.
Cybersecurity professionals commonly distinguish between passive and active eavesdropping. Passive eavesdropping involves quietly observing communications without changing the data or interfering noticeably with network activity. This type of attack can be difficult to detect because normal traffic may continue flowing while information is secretly collected. Active eavesdropping involves greater interference, such as placing an attacker-controlled system between two legitimate parties or redirecting communications through an unauthorized location. The attacker may monitor, modify, or inject information while trying to remain unnoticed. Both approaches threaten confidentiality, but active attacks can additionally undermine data integrity. Understanding this distinction helps security teams choose appropriate encryption, authentication, monitoring, and network protection strategies.
Network eavesdropping is closely connected with packet sniffing, which refers to capturing and examining packets traveling across a network. Packet analysis itself is not malicious because administrators routinely use authorized packet inspection to troubleshoot systems and diagnose performance problems. The security concern arises when someone captures traffic without permission for the purpose of discovering sensitive information. Unencrypted traffic can expose usernames, messages, application information, or other data directly. Even encrypted traffic may reveal limited metadata, such as communication endpoints or timing patterns, although the protected content should remain unreadable when strong encryption is correctly implemented. The difference between legitimate analysis and eavesdropping therefore depends heavily on authorization, intent, and the security context.
Wireless networks can create particular eavesdropping concerns because communications travel through radio signals rather than remaining confined to a physical cable. A poorly protected Wi-Fi connection may expose more information than users realize, especially when outdated security settings or insecure applications are involved. Modern WPA2 and WPA3 protections significantly improve wireless security when they are configured correctly and supported by strong credentials. Application-level encryption, such as HTTPS, adds another important layer because it protects web communications even when the underlying network cannot be fully trusted. Users should therefore avoid assuming that connecting to Wi-Fi automatically makes every application secure. Multiple security layers provide stronger protection when one individual control fails or is misconfigured.
Eavesdropping is ultimately a confidentiality problem because unauthorized people gain access to information that was intended for someone else. However, the consequences can quickly expand beyond confidentiality if intercepted data contains login credentials, session information, trade secrets, financial records, or authentication tokens. An attacker who obtains useful information may attempt account takeover, identity theft, fraud, espionage, or additional network intrusion. This makes eavesdropping more than a privacy inconvenience. It can become the first stage of a much larger security incident. Organizations should therefore protect communications as carefully as stored data and assume that sensitive information may travel through environments they do not completely control.
How Do Eavesdropping Attacks Work?
An eavesdropping attack begins when an unauthorized party gains visibility into communication that should remain private. This may happen because traffic is transmitted without adequate encryption, a network device has been compromised, wireless security is weak, or a user connects through an untrusted infrastructure point. The attacker then observes information passing through that environment and looks for data that can provide value. Depending on the situation, this could include credentials, personal conversations, session identifiers, business documents, or financial details. Strongly encrypted information is significantly harder to exploit because captured data should appear unreadable without the necessary cryptographic keys. This is why encryption in transit is one of the strongest defenses against network eavesdropping.
Passive interception generally relies on observing available network traffic rather than actively changing how the victim communicates. An attacker with unauthorized access to a suitable network segment may try to collect traffic and search for information transmitted in readable form. Because the attacker does not necessarily disrupt services, users may have no obvious indication that monitoring is occurring. This makes preventive controls particularly important. Secure protocols, encrypted applications, well-segmented networks, controlled administrative access, and properly configured switching infrastructure reduce exposure. Organizations should also limit who can access sensitive network equipment. Preventing unauthorized visibility is much more dependable than expecting users to notice a silent interception attempt after it has already begun.
Active eavesdropping can involve manipulating communication paths so information passes through a system controlled by the attacker. This broader category includes man-in-the-middle scenarios in which two legitimate parties believe they are communicating directly even though another system has inserted itself between them. If security protections fail, the unauthorized intermediary may be able to observe or modify communications. Strong certificate validation, encrypted protocols, authenticated network access, and modern browser security controls help protect against these risks. Users should take certificate warnings seriously instead of automatically bypassing them. A warning can sometimes indicate a configuration issue, but ignoring security alerts removes an important defense designed to detect suspicious or untrusted connections.
Attackers may also target network infrastructure rather than individual devices. A compromised router, wireless access point, gateway, or other intermediary can potentially provide visibility into large amounts of traffic because many communications pass through it. This is why router security is an important part of preventing eavesdropping. Default administrative passwords should be replaced, firmware should be updated, unnecessary remote management should be disabled, and configuration changes should be monitored. Business networks should apply role-based administrative access and maintain secure backups of important configurations. Infrastructure compromise can affect many users simultaneously, making centralized network devices particularly valuable targets. Strong device management therefore protects more than the hardware itself; it protects the communications relying on that hardware.
Eavesdropping can also involve software running directly on a compromised endpoint. Malware on a laptop or smartphone may capture information before it becomes encrypted or after it has been decrypted for the legitimate user. In that situation, even strong network encryption cannot completely protect the data because the attacker has gained access to one endpoint of the conversation. Endpoint security therefore complements encryption rather than replacing it. Updated operating systems, application patching, anti-malware protections, restricted administrative privileges, and careful software installation practices reduce this risk. Effective defenses protect the full communication path, including the sender, receiver, applications, network connections, and infrastructure between them.
Common Types of Eavesdropping Attacks and Examples
Packet sniffing is one of the most commonly discussed forms of network eavesdropping. It involves capturing network packets and examining the information they contain, usually through specialized network analysis software. Security teams legitimately use packet inspection to troubleshoot connectivity, investigate incidents, and understand application behavior. Unauthorized sniffing becomes a threat when someone collects communications without permission and searches them for confidential information. Traffic transmitted through old or insecure protocols can be particularly vulnerable because its contents may not be encrypted. Modern organizations should replace insecure services with encrypted alternatives wherever practical. The goal is to ensure that even if traffic is intercepted, the sensitive content remains protected and difficult for an unauthorized observer to use.
Man-in-the-middle attacks represent another major eavesdropping risk because they can place an unauthorized intermediary between two communicating systems. Consider a user attempting to connect to a legitimate service while another system secretly interferes with the communication path. Without proper authentication and encryption, the intermediary might observe information exchanged by both parties. Modern HTTPS and certificate validation are designed partly to make this type of interception more difficult. Applications should validate certificates correctly instead of accepting untrusted identities automatically. Users should also avoid bypassing browser warnings simply to reach a page more quickly. Secure communication depends not only on encrypting information but also on confirming that the intended recipient is genuine.
Wi-Fi eavesdropping can occur when wireless communication is inadequately protected or users rely on untrusted public networks. Airports, cafés, hotels, shopping centers, and conference venues commonly provide public Wi-Fi, but users may not always know who operates a particular network or how securely it is configured. An attacker may create a misleading access point name that resembles a legitimate service, hoping users connect without verification. Organizations can reduce this risk by training employees to confirm official networks and use approved secure connections when handling sensitive data. Personal hotspots can sometimes provide a safer alternative. The broader lesson is that network names alone should not automatically establish trust.
Session-related interception creates additional risk when attackers obtain information that applications use to recognize authenticated users. Modern websites typically rely on secure session mechanisms so users do not need to enter credentials on every page. If sensitive session information is exposed through insecure applications, malware, or weak implementation, unauthorized access may become possible even without knowing the original password. HTTPS, secure cookie settings, short session lifetimes for sensitive services, and reauthentication for high-risk actions can reduce the impact. Users should also sign out from shared devices and avoid storing sensitive sessions where unauthorized people have physical access. Good session management prevents captured authentication information from remaining useful indefinitely.
Voice, video, messaging, and Internet of Things communications can also become eavesdropping targets. Smart speakers, cameras, collaboration platforms, internet-connected phones, and other devices may process sensitive conversations or environmental information. Security depends heavily on software updates, encryption, authentication, device configuration, and how vendors protect data in transit. Default credentials or neglected firmware can turn convenient connected devices into weak points within a network. Businesses should inventory IoT devices rather than allowing unknown equipment to connect indefinitely. Separating less-trusted devices from critical business systems can further limit exposure. Eavesdropping prevention therefore extends well beyond laptops and websites to nearly every connected technology that transmits information.
Major Risks and Consequences of Cyber Eavesdropping
Credential theft is one of the most serious potential consequences of successful eavesdropping. If login information is transmitted or exposed insecurely, attackers may obtain usernames, passwords, or other authentication data that allows them to access accounts. Compromised credentials can then be reused against email, cloud platforms, financial systems, or business applications, particularly when users recycle passwords across services. Strong encryption greatly reduces the chance that credentials can simply be read from intercepted network traffic. Password managers and unique passwords limit the damage if one account is compromised. Multifactor authentication adds another layer because possession of the password alone may no longer be sufficient to complete a login.
Financial information can also be extremely valuable to attackers. Payment details, banking information, invoices, transaction records, and account credentials may all become targets when sensitive business or consumer communications are intercepted. Even when complete payment card information is not exposed, business correspondence can reveal enough context for invoice fraud or targeted social engineering. Attackers may learn who authorizes payments, which suppliers an organization uses, or when major transactions are expected. Security teams should therefore consider metadata and business context sensitive as well as obvious financial credentials. Encryption, verified payment procedures, and out-of-band confirmation for unusual requests can make intercepted information less useful for fraud.
Corporate espionage represents another serious risk for businesses handling research, intellectual property, strategic plans, customer information, or confidential negotiations. Eavesdropping may allow unauthorized parties to gather competitive intelligence without directly stealing files from a central server. Private conversations, remote meetings, emails, and network communications can all reveal commercially sensitive information. Organizations working with valuable intellectual property should classify information and apply stronger safeguards to the most sensitive communication channels. Remote employees should receive clear guidance about secure networks and approved collaboration tools. Protecting trade secrets requires recognizing that information can escape during transmission as well as through traditional file theft.
Personal privacy can be damaged even when intercepted information does not immediately create financial loss. Messages, browsing activity, account details, personal photos, health-related communications, and other private information may reveal intimate aspects of someone’s life. Attackers could potentially use this information for harassment, impersonation, blackmail, or targeted scams. The damage may continue long after the original interception because digital information can be copied and distributed easily. Users should therefore avoid assuming that only banking or password information needs protection. Privacy-focused security means protecting ordinary communications as well as obviously valuable credentials. Strong encryption helps preserve the confidentiality of everyday digital life.
Organizations can also face operational, legal, contractual, and reputational consequences when eavesdropping exposes protected information. Customers may lose confidence in a company that fails to safeguard sensitive communications, while business partners may reconsider integrations or data-sharing relationships. A serious interception incident can require forensic investigation, credential resets, notification procedures, legal review, and substantial remediation work. Service disruption may follow if compromised infrastructure must be isolated or rebuilt. Prevention is therefore usually far less disruptive than responding after information has already leaked. Building secure communications into normal operations reduces both technical exposure and the broader business impact that can follow a successful cyberattack.
How to Detect Possible Eavesdropping and Network Interception
Detecting passive eavesdropping can be difficult because a successful observer may not need to create noticeable network disruption. Users should therefore avoid expecting obvious warning signs such as dramatically slower internet speeds or frequent application crashes. Silent interception can occur while services continue functioning normally. Organizations need network monitoring, endpoint visibility, access controls, and security analytics that identify unusual behavior rather than relying entirely on user reports. Logs from routers, authentication systems, firewalls, wireless controllers, and endpoint security platforms can provide useful evidence. Baseline monitoring helps teams recognize deviations from normal network behavior. The absence of visible problems should never be interpreted as proof that communications cannot be monitored.
Unexpected certificate warnings can be an important indication that something about a supposedly secure connection is wrong. Browsers and applications validate digital certificates partly to verify that users are communicating with the intended service. A warning may result from an expired certificate or legitimate configuration error, but it can also signal an untrusted or intercepted connection. Users should not simply click through certificate warnings when accessing sensitive systems. Business employees should report unexpected warnings to their IT or security team. Administrators can then determine whether the cause is benign or suspicious. Treating certificate alerts seriously preserves one of the key protections built into encrypted web communication.
Unknown devices appearing on a home or business network can also deserve investigation. Modern routers and wireless management systems often display lists of connected devices, including names, addresses, and connection details. An unfamiliar entry does not automatically indicate an attacker because phones can use randomized MAC addresses and many smart devices have unclear manufacturer names. However, repeated unknown connections should not be ignored. Users can review device inventories, update Wi-Fi credentials when necessary, and remove obsolete equipment from remembered networks. Businesses should use network access controls appropriate to their environment. Accurate asset inventories make it much easier to distinguish legitimate equipment from suspicious connections.
Security teams can also watch for unusual network configuration changes or unexpected infrastructure behavior. Unauthorized DNS changes, newly created administrative accounts, modified router settings, or unexplained wireless access points may indicate that someone is attempting to redirect or observe traffic. Configuration monitoring and centralized logging can highlight these changes before they remain unnoticed for months. Organizations should restrict administrative privileges and require strong authentication for network management systems. Important changes should be documented so security staff can distinguish authorized maintenance from suspicious activity. The ability to detect tampering depends heavily on knowing what the correct configuration should look like in the first place.
Endpoint alerts may reveal eavesdropping-related malware or tools running where they should not be present. Unexpected processes, unusual network connections, unauthorized software installations, or security products being disabled can all justify investigation. Individual users should avoid trying to diagnose advanced compromise through random software downloads because unnecessary tools can create additional risk. Keeping built-in security features enabled and seeking qualified technical help is usually safer. Organizations can use endpoint detection and response platforms to correlate suspicious behavior across multiple devices. Detection works best when endpoint data is combined with network and identity information. A single alert may seem harmless, while several related signals can reveal a larger interception attempt.
How Individuals Can Prevent Eavesdropping Attacks
Using websites and applications that encrypt communications is one of the most important ways individuals can protect themselves from digital eavesdropping. Modern websites should use HTTPS so information exchanged between the browser and web server is protected while traveling across networks. Browsers usually display security indicators and warn users when certificate validation fails. People should avoid entering passwords, payment information, or other sensitive details into websites that clearly lack secure connections. Applications should also be downloaded from trusted sources because fake or modified software may bypass network protections by stealing information directly from the device. Secure communication begins with using trustworthy software and properly authenticated services.
Public Wi-Fi should be approached with reasonable caution, especially when accessing work systems, financial accounts, or other sensitive services. Users should confirm the official network name instead of connecting automatically to whichever access point appears strongest. Disabling automatic connection to unfamiliar Wi-Fi networks can reduce accidental exposure. A reputable VPN can provide an additional encrypted layer between the device and VPN service, which can be useful on networks the user does not fully trust. However, a VPN does not make malicious websites safe or replace HTTPS. Users should still verify the websites and applications they access. Security is strongest when multiple safeguards work together rather than relying on a single tool.
Home Wi-Fi networks should use modern wireless security, preferably WPA2 or WPA3 when supported by available equipment. Weak or outdated encryption settings should be replaced, and default router administration passwords should be changed immediately. The Wi-Fi password itself should be long enough to resist easy guessing and should not be shared unnecessarily. Router firmware should be kept updated because manufacturers may release fixes for security vulnerabilities. Features such as remote administration should be disabled when they are not needed. A home router is the gateway for many devices, making its security important for laptops, phones, smart televisions, cameras, and other connected equipment.
Multifactor authentication provides valuable protection when eavesdropping or another attack exposes a password. MFA requires an additional verification step, such as an authenticator application, hardware security key, or another approved factor. This means a stolen password may not be sufficient for account access. Strong, unique passwords should still be used because multifactor authentication complements password security rather than replacing it. Password managers can help users avoid repeating the same credentials across many websites. High-value accounts such as email, banking, cloud storage, and workplace systems deserve particular attention. Protecting identity credentials limits what an attacker can accomplish even if some information is intercepted.
Keeping devices updated is equally important because eavesdropping risks are not limited to network infrastructure. Operating system vulnerabilities, outdated browsers, compromised applications, and malicious extensions can all expose information before or after encryption protects it in transit. Automatic security updates should generally remain enabled where practical. Users should remove software they no longer need and review permissions granted to browser extensions or mobile applications. Screen locks and device encryption provide additional protection if a phone or laptop is physically lost. Cybersecurity works as a connected system: secure devices, secure networks, secure applications, and strong account protection collectively make successful eavesdropping considerably more difficult.
How Businesses Can Reduce Eavesdropping Risks
Businesses should begin by requiring strong encryption for sensitive communications throughout their environment. Web applications should use modern TLS configurations, while remote administration protocols should use secure encrypted alternatives rather than legacy plaintext services. Email security, collaboration platforms, APIs, database connections, and internal application traffic should also be reviewed rather than assuming encryption only matters for public websites. Internal networks are not automatically trustworthy because compromised devices can exist inside an organization. Encrypting important internal communications limits what an attacker can learn after gaining partial network access. Security architecture should therefore protect data based on sensitivity rather than simply whether it is traveling inside or outside the office.
Network segmentation can reduce the number of systems exposed if one part of a network becomes compromised. Employee workstations, servers, guest Wi-Fi, IoT equipment, development systems, and highly sensitive infrastructure do not always need unrestricted communication with one another. Separating these environments can limit an unauthorized observer’s ability to move freely or access valuable network traffic. Access between segments should follow legitimate business requirements rather than broad default permissions. Zero-trust principles can strengthen this model by requiring authentication and authorization based on identity and context. Segmentation is not a substitute for encryption, but the combination makes widespread eavesdropping and lateral movement more difficult.
Organizations should also secure wireless infrastructure through strong authentication, modern encryption, controlled access points, and ongoing monitoring. Corporate Wi-Fi should not depend on widely shared passwords when stronger enterprise authentication is practical. Guest networks should be separated from internal business systems so visitors cannot directly access sensitive resources. Security teams should periodically identify unauthorized or unexpected wireless access points near business locations. Employees need clear instructions about connecting to corporate networks and reporting suspicious wireless behavior. Remote staff should use approved secure access methods when reaching company resources from outside the office. Wireless security should be treated as part of enterprise networking rather than as a simple convenience service.
Identity and access management can significantly reduce the consequences of intercepted credentials. Organizations should require multifactor authentication for important systems and prioritize phishing-resistant methods for high-risk accounts where practical. Privileged access should be limited to employees who genuinely need administrative capabilities. Service accounts, API credentials, and machine identities should receive the same attention as human user accounts because they can provide valuable access when compromised. Password reuse should be discouraged through approved password managers and identity systems. Session lifetimes and authentication policies should reflect the sensitivity of each application. Reducing unnecessary privilege limits what an attacker can reach even after obtaining usable authentication information.
Continuous monitoring, security training, and incident response planning complete the defensive picture. Employees should understand why certificate warnings, suspicious Wi-Fi networks, unexpected login prompts, and unusual account activity deserve attention. Security teams should collect relevant logs and monitor network, identity, and endpoint events for patterns that could indicate interception or infrastructure compromise. Regular security assessments can identify outdated protocols, weak wireless configurations, or exposed administrative interfaces before attackers find them. Incident response plans should explain how compromised accounts and network devices will be isolated and investigated. Organizations that combine prevention, detection, and response are better prepared because no individual cybersecurity control can guarantee complete protection.
Frequently Asked Questions About Eavesdropping in Cybersecurity
What does eavesdropping mean in cybersecurity?
Eavesdropping in cybersecurity means secretly intercepting or monitoring digital communications without authorization. It can involve network traffic, Wi-Fi transmissions, messages, credentials, calls, or other data moving between systems.
What is an example of a cyber eavesdropping attack?
One example is an unauthorized person monitoring insecure network traffic to collect information being transmitted without adequate encryption. Another is a man-in-the-middle situation in which an attacker interferes with the communication path between two legitimate systems.
Can HTTPS prevent eavesdropping?
HTTPS greatly reduces eavesdropping risk by encrypting information between a browser and the authenticated website. It does not protect against every threat, such as malware already installed on the user’s device or a compromised website itself.
Does a VPN protect against eavesdropping?
A reputable VPN encrypts traffic between your device and the VPN service, which can reduce exposure on untrusted networks such as public Wi-Fi. It should still be combined with HTTPS, updated devices, strong authentication, and careful browsing habits.
How can businesses prevent network eavesdropping?
Businesses can reduce the risk through strong encryption, secure Wi-Fi, network segmentation, multifactor authentication, restricted administrative access, modern security protocols, endpoint protection, and continuous monitoring. Regular updates and employee security training provide additional protection against interception attempts.